Roseline Ilori: Trust Must Remain at the Heart of Digital Innovation
The Bridge57 Solutions CEO and digital trust leader speaks on data protection, AI governance, cybersecurity and the urgent need for responsible technology adoption as Nigeria’s digital economy evolves.
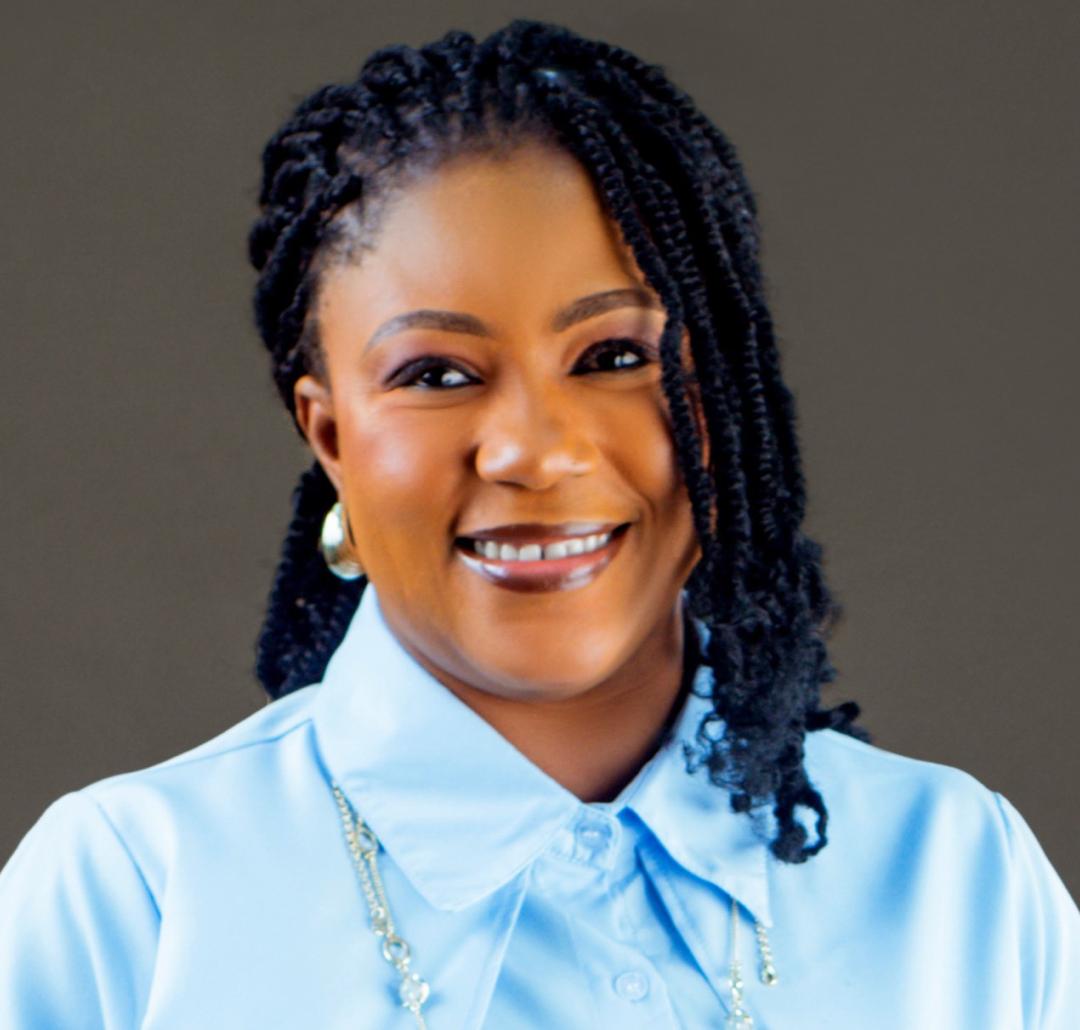
Roseline Ilori, CEO of Bridge57 Solutions Limited, is a Pan-African technology and compliance leader with over two decades of experience spanning digital transformation, data privacy, cybersecurity, AI governance and digital trust.
A former CEO of MTech Communications Plc, she has led digital innovation across Nigeria and 11 other African countries. She is also Co-Founder and Trustee of Women in Data Privacy and Deputy Chairperson, ICT Sectorial Group, Lagos Chamber of Commerce and Industry (LCCI).
In this interview with Don Pedro Aganbi, Ilori discusses data protection, AI governance, cybersecurity, digital trust and the responsibility of businesses to protect the data entrusted to them.
1. Can you take us through your journey into the technology industry?
My journey began with a foundation in computer engineering and an interest in how technology solves practical problems. Over the years, I worked across telecommunications, mobile services and digital platforms, including serving as CEO of MTech Communications.
Those experiences showed me the opportunities technology can create across Africa, but also how much a business depends on people trusting the systems behind it. Today, as founder and CEO of Bridge57 Solutions, my work sits at the intersection of data protection, cybersecurity, AI governance and digital trust. For me, the thread connecting those areas is simple: innovation creates lasting value when people can use it with confidence.
2. Tell us about Bridge57 and your mission to the industry, including the gap you are trying to fill?
Bridge57 helps organisations build and grow digital services responsibly.
We work with businesses on data protection compliance, cybersecurity, AI governance, training and digital solutions, drawing on our experience in telecommunications and technology delivery. We are a licensed Data Protection Compliance Organization (CDPO) by the Nigerian Data Protection Commission (NDPC).
We are an Accredited Training Organization for the Certified Data Protection Officers Training.
The gap we see is that many organisations treat these as separate assignments. One team handles a compliance filing, another buys security tools, and employees start using AI without clear guidance.
Yet customers experience the organisation as one entity. If their data is misused, exposed or used to make an unfair decision, those internal divisions mean very little to them.
Our mission is to help organisations connect the pieces: understand the data they hold, protect it, use it responsibly and make trust part of how they operate. That is how compliance becomes a business strength rather than an annual exercise.
3. Data protection compliance in Nigeria is sometimes perceived as a box-ticking exercise. What can the NDPC do differently to drive deeper and more measurable compliance across the private and public sectors?
The NDPC has helped establish a stronger foundation through the Nigeria Data Protection Act, 2023 and its implementation guidance. The next step is to make the quality of compliance more visible. Filing a report matters, but it should lead to a more important question: what risks did the organisation find, and what did it fix?
I would like to see clearer, sector specific guidance and more emphasis on evidence of working controls: whether organisations know what personal data they hold, have tested their response to incidents, train staff, assess high-risk projects before launch and resolve individuals’ complaints promptly. The Commission could also publish anonymized trends from audits and enforcement, so organisations can learn from recurring failures.
This approach should apply to public institutions as well as private companies. People should be able to expect responsible handling of their data wherever they provide it. At the same time, smaller businesses need practical guidance proportionate to their resources. The goal is compliance that changes behaviour and reduces harm.
4. With AI and fintech growing rapidly, what are the biggest emerging privacy risks, and are organisations prepared to manage them?
One major risk is that data collected for one purpose quietly begins to serve many others. A financial transaction can generate information about a person’s location, habits and relationships. When that information is combined with AI, it can shape decisions about credit, fraud, pricing or access to services.
Organisations must be able to explain what data is used, why it is needed and how people can challenge a consequential decision. Another immediate risk is uncontrolled use of AI tools.
An employee may paste customer
records, financial information or confidential business material into an external system without understanding where that information goes. We also need to watch for biased outcomes, excessive data collection, weak vendor oversight and fraud that becomes more convincing through AI-generated content.
Preparedness is uneven. Some organisations have capable privacy and security teams, but many are adopting tools faster than they are setting rules for them. Leadership should know which AI systems are in use, assess their risks before deployment, restrict sensitive data from unapproved tools and ensure meaningful human review of decisions that affect people.
5. Experts say Nigeria’s data protection framework is not keeping pace with digital transformation. Do you agree, and where should the NDPC do more?
I would distinguish between the law and its application. The Nigeria Data Protection Act, 2023 gives us a foundation. Technology will continue to change faster than legislation, so we
should not assume that every new risk requires a new law. What organisations often need is timely, practical guidance on applying existing principles to new uses of data.
I would welcome more detailed guidance on AI systems, automated decisions, children’s data, biometric information, data sharing across platforms and the responsibilities of technology vendors.
The NDPC should continue engaging innovators, industry groups and other regulators, because a single digital service can raise privacy, financial, communications and cybersecurity questions at the same time.
We should also measure whether guidance works in practice. Can a small business understand what it must do? Can an individual exercise their rights without difficulty? Can an
organisation identify and correct a harmful use of data before it affects thousands of people? Those are useful tests of whether the framework is keeping pace.
6. What practical steps can businesses take to build a genuine culture of privacy?
Start by knowing what personal data you collect, why you collect it, who can access it, whom you share it with and when you delete it. Many problems begin because an organisation cannot answer those basic questions.
Then make privacy part of everyday decisions. Review a new product, marketing campaign or AI tool before it goes live. Limit access to staff who need it. Check vendors carefully. Train
employees with examples from their actual jobs, not just a slide deck they see once a year.
Give customers clear information and a straightforward way to raise concerns or exercise their rights. Leadership matters most. If the board and management ask about data risks, fund the necessary controls and respond seriously when something goes wrong, staff will understand that privacy is part of the organization’s standards. Culture is what people do with data when no audit is taking place.
7. As we approach the 2027 elections, what role should data protection, cybersecurity and responsible data governance play in a secure and trusted electoral ecosystem?
Elections depend on public confidence, and that confidence includes how voter information
and election systems are handled.
Electoral bodies, political parties, campaign teams, technology providers and others who process personal data should collect only what they need, protect it against unauthorized access and be clear about how it is used.
Cybersecurity is essential to the availability and integrity of systems and communications. It calls for access controls, testing, monitoring, incident plans and coordination before an emergency occurs.
Data governance addresses another set of questions: who is allowed to use voter or supporter information, for what purpose, for how long, and with what accountability?
We should be especially alert to leaked databases, deceptive messages, impersonation and the use of personal data to manipulate voters. No single safeguard can guarantee trust in an election. But protecting people’s data, securing critical systems and communicating transparently when issues arise are necessary parts of a resilient process.
8. Finally, what is your message to Nigerian businesses about protecting the data they hold?
People give businesses their data because they need a service and expect that information to be handled with care. That creates a responsibility, whether the business holds fifty
customer records or fifty million.
Businesses should not wait for a breach or a regulatory notice to find out what data you have. Know it, secure it, limit its use, train the people who handle it and be honest with customers.
As AI opens new possibilities, they need to ask whether a proposed use of data is fair and necessary, not merely whether it is technically possible.
Trust is difficult to rebuild once it is lost. The businesses that protect it will be better placed to earn lasting customer relationships and participate in Nigeria’s digital growth.
Comments (0)
No comments yet. Be the first to join the conversation!
Leave a Reply
Your email address will not be published. Required fields are marked *